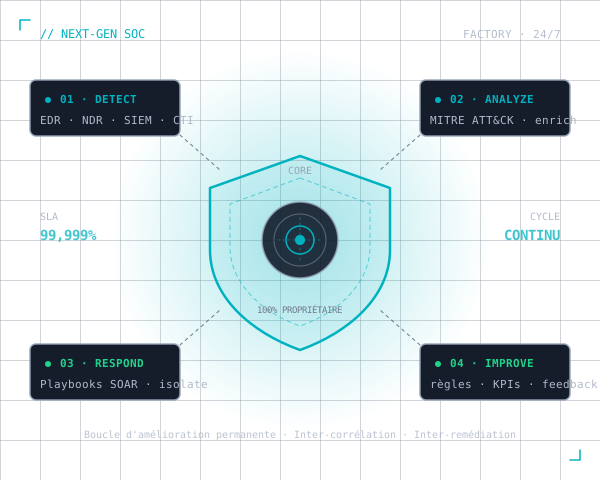
A full cycle, with no blind spot.
Four disciplines coordinated around an orchestrating core: Detect, Analyze, Respond, Improve. A closed loop covering the whole life of an incident — and learning as it goes.
- Sources: EDR · NDR · SIEM · CTI
- Core: sovereign orchestrator
- Response: SOAR playbooks
- Continuous improvement loop
Three commitments that shape the service.
Stability
Named, permanent points of contact.
Agility
A range of multi-skilled profiles.
Efficiency
A SOC wired into our clients' environments.
24 hours a day, 365 days a year.
No window of unavailability. Our Security Factory runs continuously, without interruption — nights, weekends and public holidays included. Your critical incidents keep no office hours, and neither does our SOC.
What we guarantee.
Clients who use the Five Nines managed services get:
A dedicated service, 24 hours a day, 365 days a year
Straightforward deployment
lower cost · less time
Dedicated security analysts
from alert to remediation
A single integrated platform
Minimal reaction time
fast triage
Fast action and incident resolution
Automated operations
Remediation processes adapted
to your needs and constraints
Continuous improvement of the service
A wide choice of trusted partners
From alert to remediation.
Automating the time-consuming work sits at the heart of our SOC. Inter-correlation and inter-remediation are the foundations of how we work.
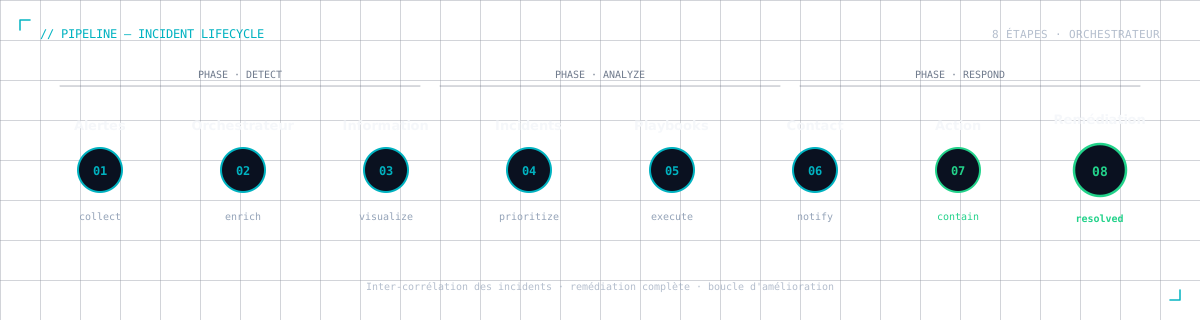
- Step01
Alerts
Centralised, correlated and systematic analysis of every alert raised.
- Step02
Orchestrator
Contextual enrichment and cross-correlation of events.
- Step03
Information
Enriched data presented to analysts quickly and in summary form.
- Step04
Incidents
Assignment and prioritisation by level of criticality.
- Step05
Playbooks
Playbooks run automatically, with manual control available.
- Step06
Contact
Real-time communication with the client to assess the threat.
- Step07
Action
Execution following the operating model agreed with the client.
- Step08
Correlation & remediation
Cross-correlated incident handling and full remediation.
A question? A project?
Our security specialists are available to you. A NextGen-SOC demonstration, an audit, or simply a conversation — start here.