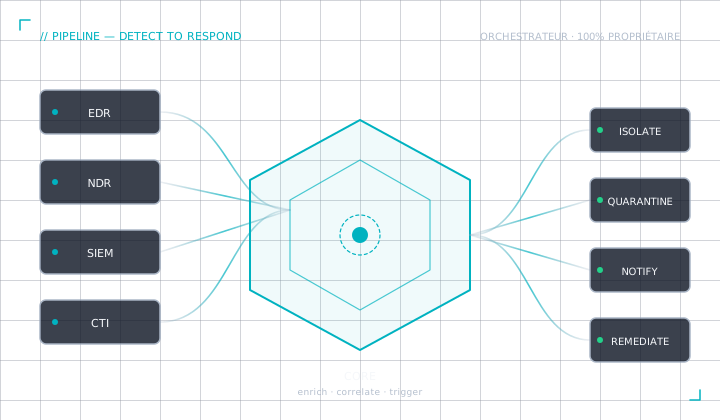
The team that monitors and responds to incidents. Our next-generation SOC automates collection, correlation, enrichment and remediation. Real-time monitoring of networks, servers, endpoints, databases and applications through our orchestrator.
The orchestrator behind our SOC.
No product on the market joined the bricks of a SOC the way we needed. Our NextGen-SOC is therefore built on the Meta Orchestrator, built by our French partner sudoexec and operated by our analysts.
It is what carries inter-enrichment and inter-remediation: an alert raised in one tool is completed with what every other tool knows, and a response decision applies across the whole chain at once.
- 100% compatible with partner interfaces
- Built in France by sudoexec, operated by our analysts
- No dependency on a non-European vendor
AI & machine learning
Measured, targeted use of AI and learning algorithms to handle both basic and advanced threats through real-time data analysis.
Cloud infrastructure
Cloud services — energy efficiency, smooth deployment and complete security solutions.
Advanced threat intelligence
Real-time analysis of emerging threats and proactive threat hunting.
Immediate automation
Routine work — vulnerabilities, patching — executed at industrial scale, freeing the teams for the complex subjects.
Zero Trust compliance
ISO 27001 certified services, with internal and external traffic verified along Zero Trust principles.
An auditable, customisable solution, shaped to each client's own requirements.
The solutions we operate.
We only integrate technology we run ourselves. Each page says what the product does, what it does not do, and what we add to it.
- METAsudoexec
Meta Orchestrator
The layer that sits above endpoint, SIEM, identity, email and network: every signal is enriched by all the others, and every response decision applies across the whole chain at once.
Explore - EDR

Falcon — Endpoint Detection & Response
Detection and response on endpoints, the foundation of any defence chain. One lightweight agent, one console, and the ability to isolate a machine before the attacker spreads.
Explore - ITP

Falcon Identity Threat Protection
Monitoring of Active Directory and cloud directories: privilege escalation, forgotten service accounts, abnormal authentication, and conditional blocking in real time.
Explore - SIEM

Falcon Next-Gen SIEM
The collection and correlation platform that brings together endpoint, identity, cloud and third-party data, and on which our analysts work every day.
Explore - SIEM

Log360
Unified log management, Active Directory auditing, behavioural analytics and compliance, on premises or in the cloud. A credible alternative when sovereignty or budget dictates.
Explore - IAM

AD360 — identity protection
Identity management and auditing across Active Directory, Entra ID and Microsoft 365: provisioning, access reviews, self-service password reset and step-up authentication.
Explore - MAIL

Email protection
Advanced filtering, link rewriting, attachment detonation, impersonation detection, evidential archiving and user training.
Explore - SASE

Zero Trust Exchange — SASE
Secure web gateway, firewall as a service, cloud access broker and Zero Trust private access, delivered from a distributed platform rather than from your own egress points.
Explore
The vocabulary of modern defence.
The eleven technical building blocks we work with day to day for our clients.
Detects and counters suspicious activity on desktops, laptops and mobile devices. Precise monitoring and advanced remediation to neutralise threats before they spread.
Broad visibility across the network to spot adversary behaviour in physical, virtual and cloud infrastructure. Identifies lateral movement and suspicious communication.
Protected web access for users. Guards against threats and infection by inspecting traffic and filtering malicious packets before they reach internal systems.
Cloud firewall with access control, URL filtering, advanced threat protection, IPS and DNS security.
Implements a Zero Trust model: internal and external threats treated alike, strict verification before any access to resources.
Security and compliance for cloud-native applications. Combines CSPM, CIEM, IAM, CWPP and data protection in one platform.
Control over public cloud usage and policy compliance. Fits into DevSecOps: static scanning, hardening, API scanning, penetration testing.
Sits between users and cloud platforms — data protection, authorisation management and visibility, fine-grained access control.
Detects and neutralises threats inside cloud software. Unified administration for physical servers, VMs, containers and serverless functions.
Analysis of cyber threats — gathering, studying and sharing information about computer attacks.
A question? A project?
Our security specialists are available to you. A NextGen-SOC demonstration, an audit, or simply a conversation — start here.